Smoke is me glancing over your shoulder. Deep is me pulling the thread until
something unravels. Agent is me rolling up my sleeves because you clearly
weren’t going to.
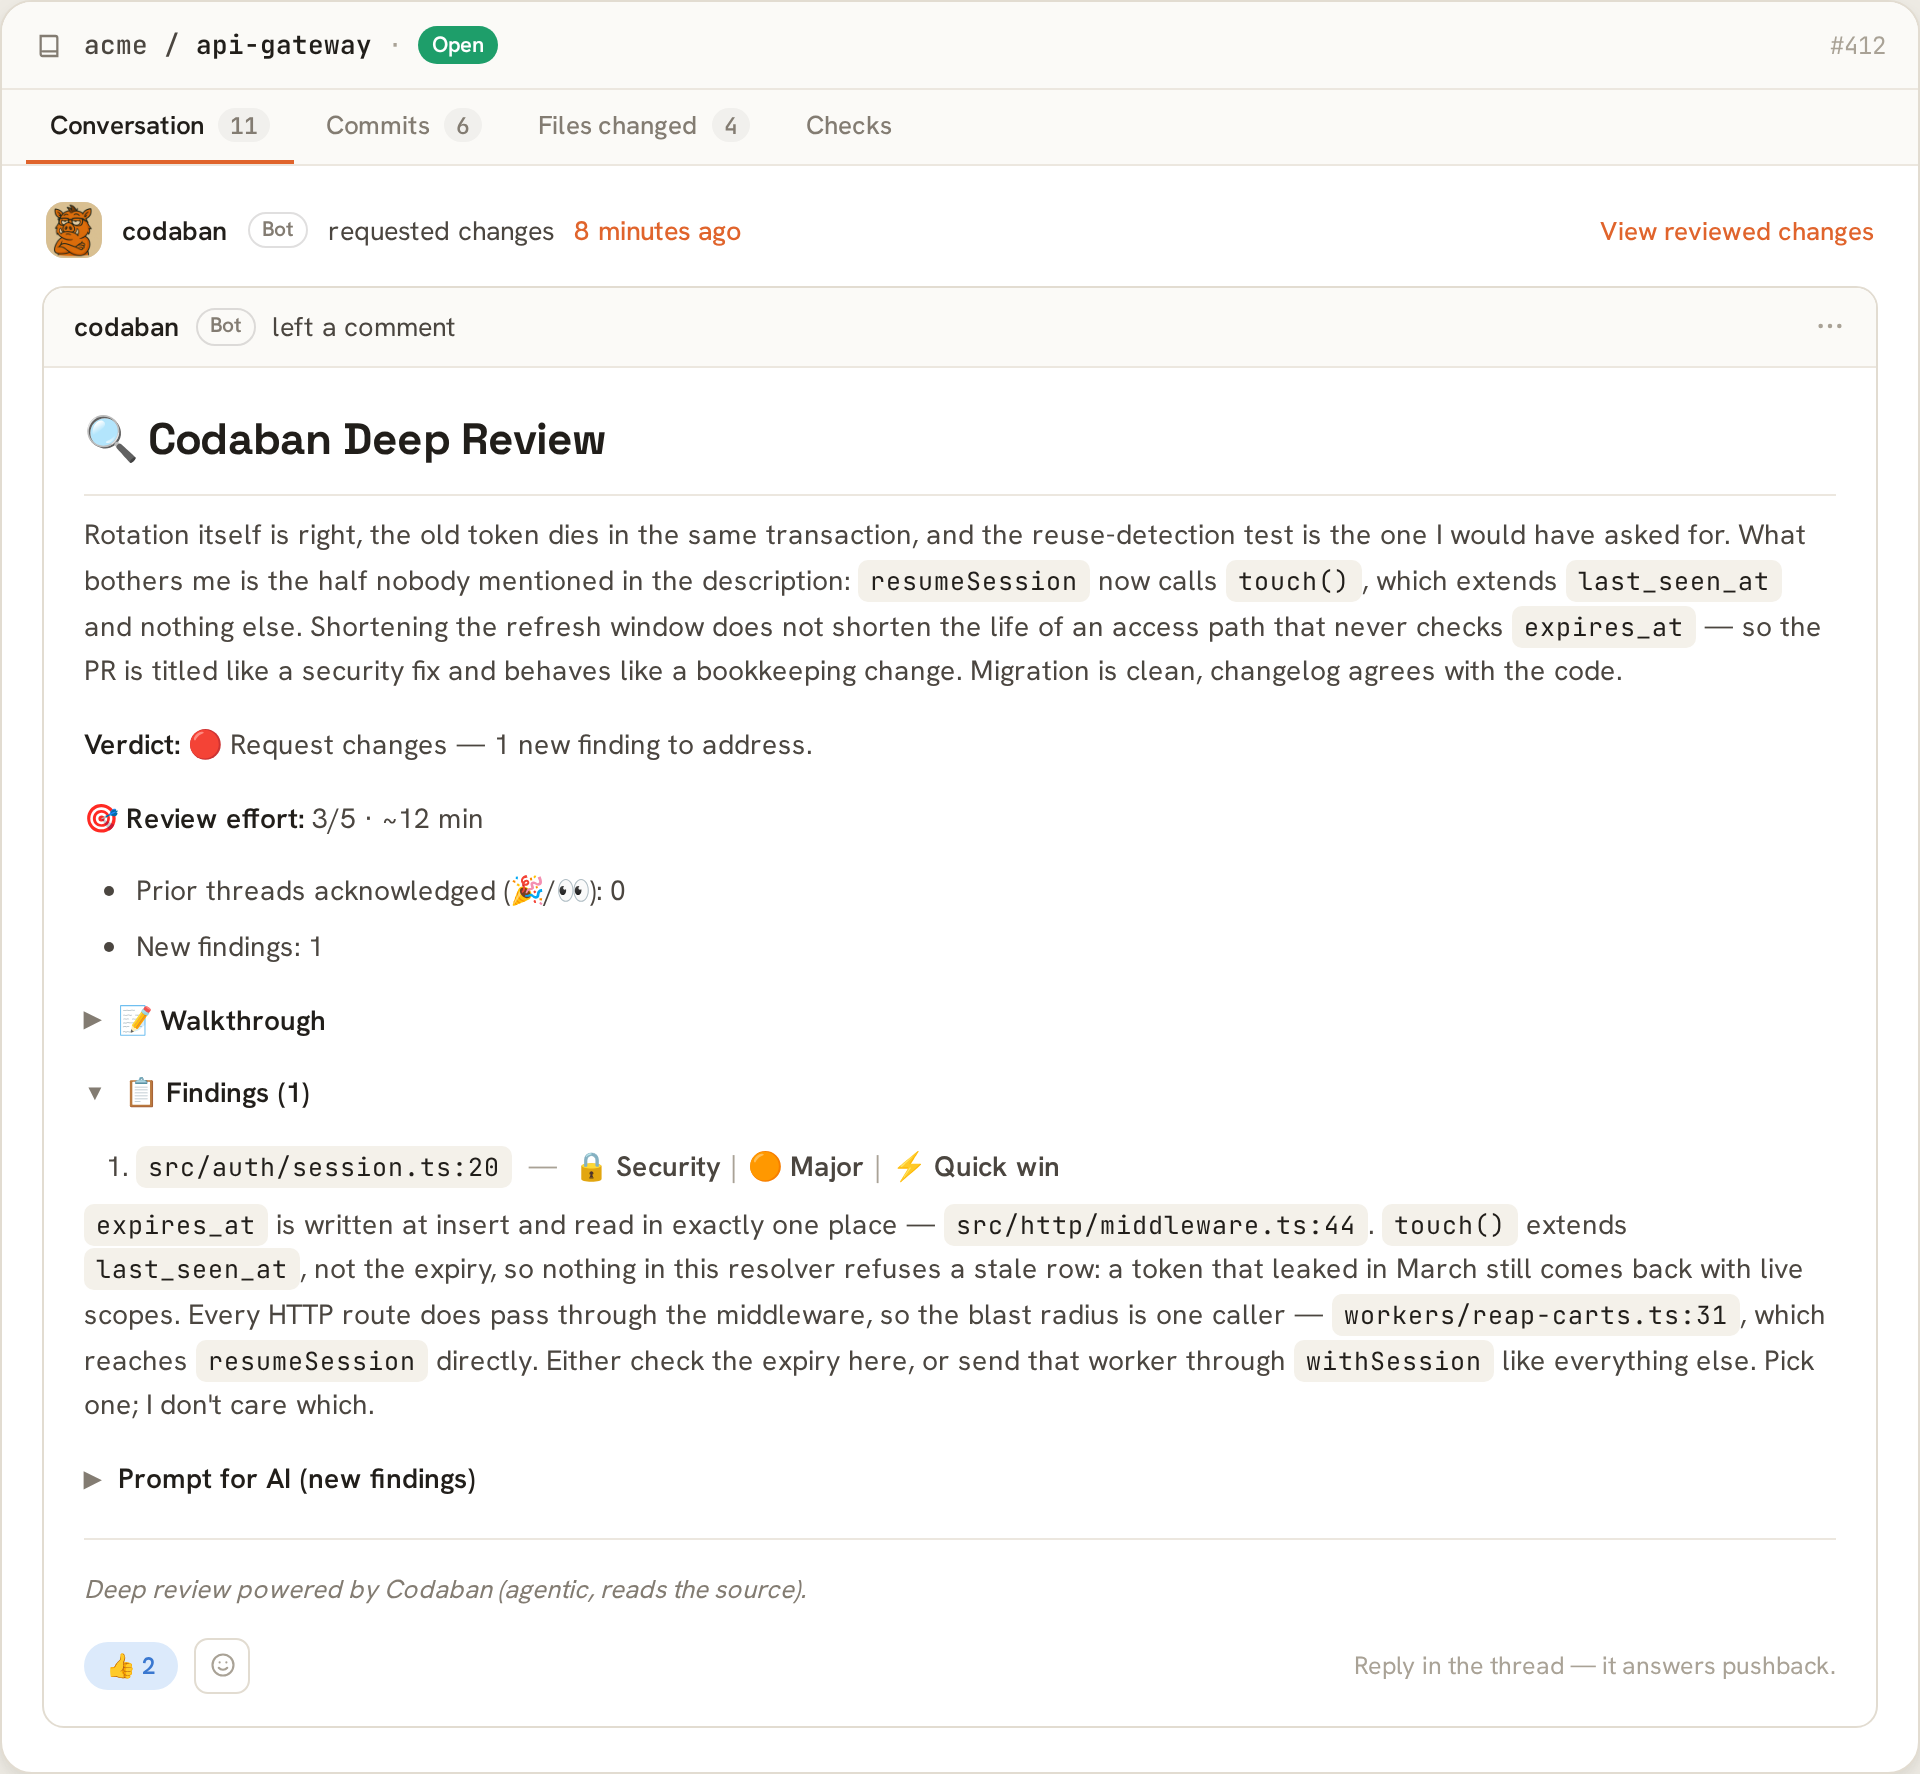
A deep review on a pull request — verdict, review effort, and the finding underneath.
Start here
Getting started
Workspace, billing account, first repository. About a minute.
Commands
The
@codaban … grammar. One comment, one run, one deliberate spend.Reviews
Smoke, deep, re-reviews, and arguing with the findings.
Agentic workflow
Plan → implement → iterate, from issue to open PR.
Connect your forge
GitHub
Install the App, pick repositories, done.
Forgejo or Gitea
Self-hosted, connected with a bot account and a token.
It takes a position
Codaban approves or requests changes, and tells you why either way. Never a silent green tick. Approve Request changes Comment Every inline finding leads with category · severity · effort, so you can triage before reading a word of it. Findings Codaban couldn’t confirm from the code alone are marked 🔍 Unverified — it can read your repository, but it never runs it. Those never request changes on their own.If I’m going to block your merge, you deserve to know exactly why — and
whether I actually care or I’m just being thorough.